
 2026-07-24

Operation CameraSwarm — 某视频监控厂商设备大规模沦陷
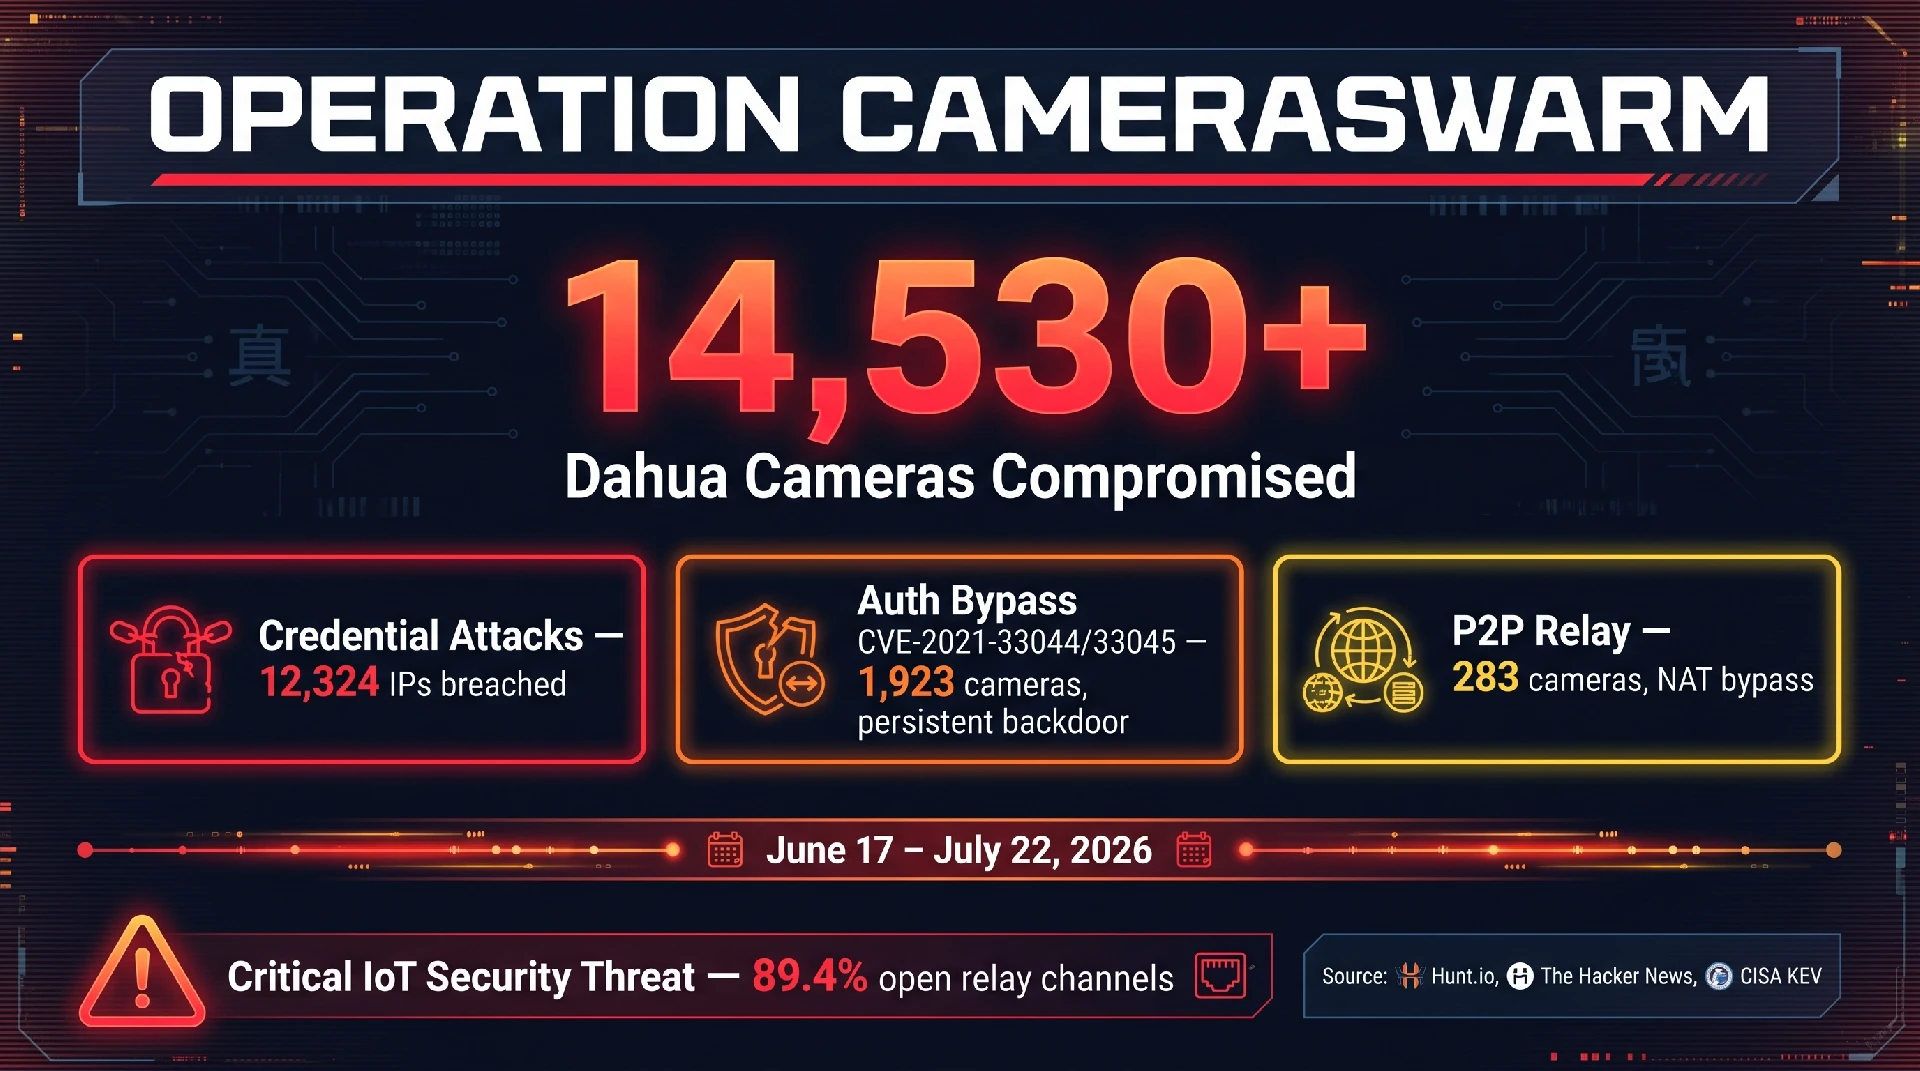
2026年6月17日~7月22日,安全公司 Hunt.io 发现并重建了一起大规模摄像头入侵行动,代号 Operation CameraSwarm:
维度数据
累计攻陷设备 : 14,530+ 台某厂商 IP 摄像头及 NVR
攻击路径① :弱口令暴破 — 12,324 个独立 IP,13,229 条记录
攻击路径② :身份绕过漏洞 CVE-2021-33044/33045 — 1,923 台,植入重启/恢复出厂均存留的后门账号
攻击路径③ :利用厂商自带的 P2P 云中继(Easy4IP),仅凭序列号就能穿透 NAT 隔离 283 台设备
值得注意的是第三条:云中继本身设计了"设备先认证会话"而非"中继先认证客户端"的逻辑漏洞——只要知道摄像头序列号,不需要任何密码就能打开一条中继通道。攻击者日志显示89.4% 的在线设备中招,而且该漏洞在2024年中之后的固件中仍未完全修复。
荷兰 AIVD/MIVD 情报机构随后确认:俄罗斯情报部门系统性劫持欧洲和乌克兰境内联网摄像头,实时监视军事运输路线和乌军部署位置。在乌克兰境内,摄像头访问权甚至被用于校准火力打击。超过 8.7 万台带已知漏洞的摄像头暴露在欧盟/NATO 成员国和乌克兰。
此事件印证了一个根本逻辑:摄像头本身的漏洞只是入口,网络接入管控缺失才是放大器!
Operation CameraSmart - A video surveillance manufacturer's equipment fell on a large scale
From June 17 to July 22, 2026, security company Hunt.io discovered and reconstructed a large-scale camera intrusion operation, codenamed Operation CameraSmart:
Dimension data
Accumulated capture of 14530+IP cameras and NVRs from a certain manufacturer
Attack path ① Weak password burst -12324 independent IPs, 13229 records
Attack path 2: Identity bypass vulnerability CVE-2021-33044/33045-1923, implanted with a backdoor account that persists after reboot/factory reset
Attack path ③ utilizes the manufacturer's built-in P2P cloud relay (Easy4IP) to penetrate NAT and isolate 283 devices with only the serial number
It is worth noting that the third point is that Yunzhong Ji has designed a logical vulnerability of "device first authentication session" instead of "relay first authentication client" - as long as the camera serial number is known, a relay channel can be opened without any password. The attacker logs show that 89.4% of online devices were compromised, and the vulnerability has not been fully fixed in firmware after mid-2024.
The Dutch AIVD/MIVD intelligence agency subsequently confirmed that Russian intelligence agencies systematically hijacked internet connected cameras within Europe and Ukraine to monitor military transportation routes and Ukrainian military deployment locations in real-time. In Ukraine, camera access rights are even used to calibrate firepower strikes. Over 87000 cameras with known vulnerabilities have been exposed in EU/ATO member states and Ukraine.
This incident confirms a fundamental logic: the vulnerability of the camera itself is only the entrance, and the lack of network access control is the amplifier!